Cyber GRC
GRC built on real security context
Stay audit-ready with evidence tied to the work your security teams already do, while proving controls are working, prioritizing cyber risk, and managing third-party exposure.


Turn security actions into GRC proof
Cyber GRC connects controls, risks, vendors, evidence, and remediation so teams can govern from what is happening in real time.
Keep governance tied to action
Connect policies, controls, owners, and issues so governance reflects the work happening across security and IT.


Close the gap between SecOps and GRC
Bring attack surface data, control health, vendor risk, evidence, remediation, and reporting into one connected workflow.
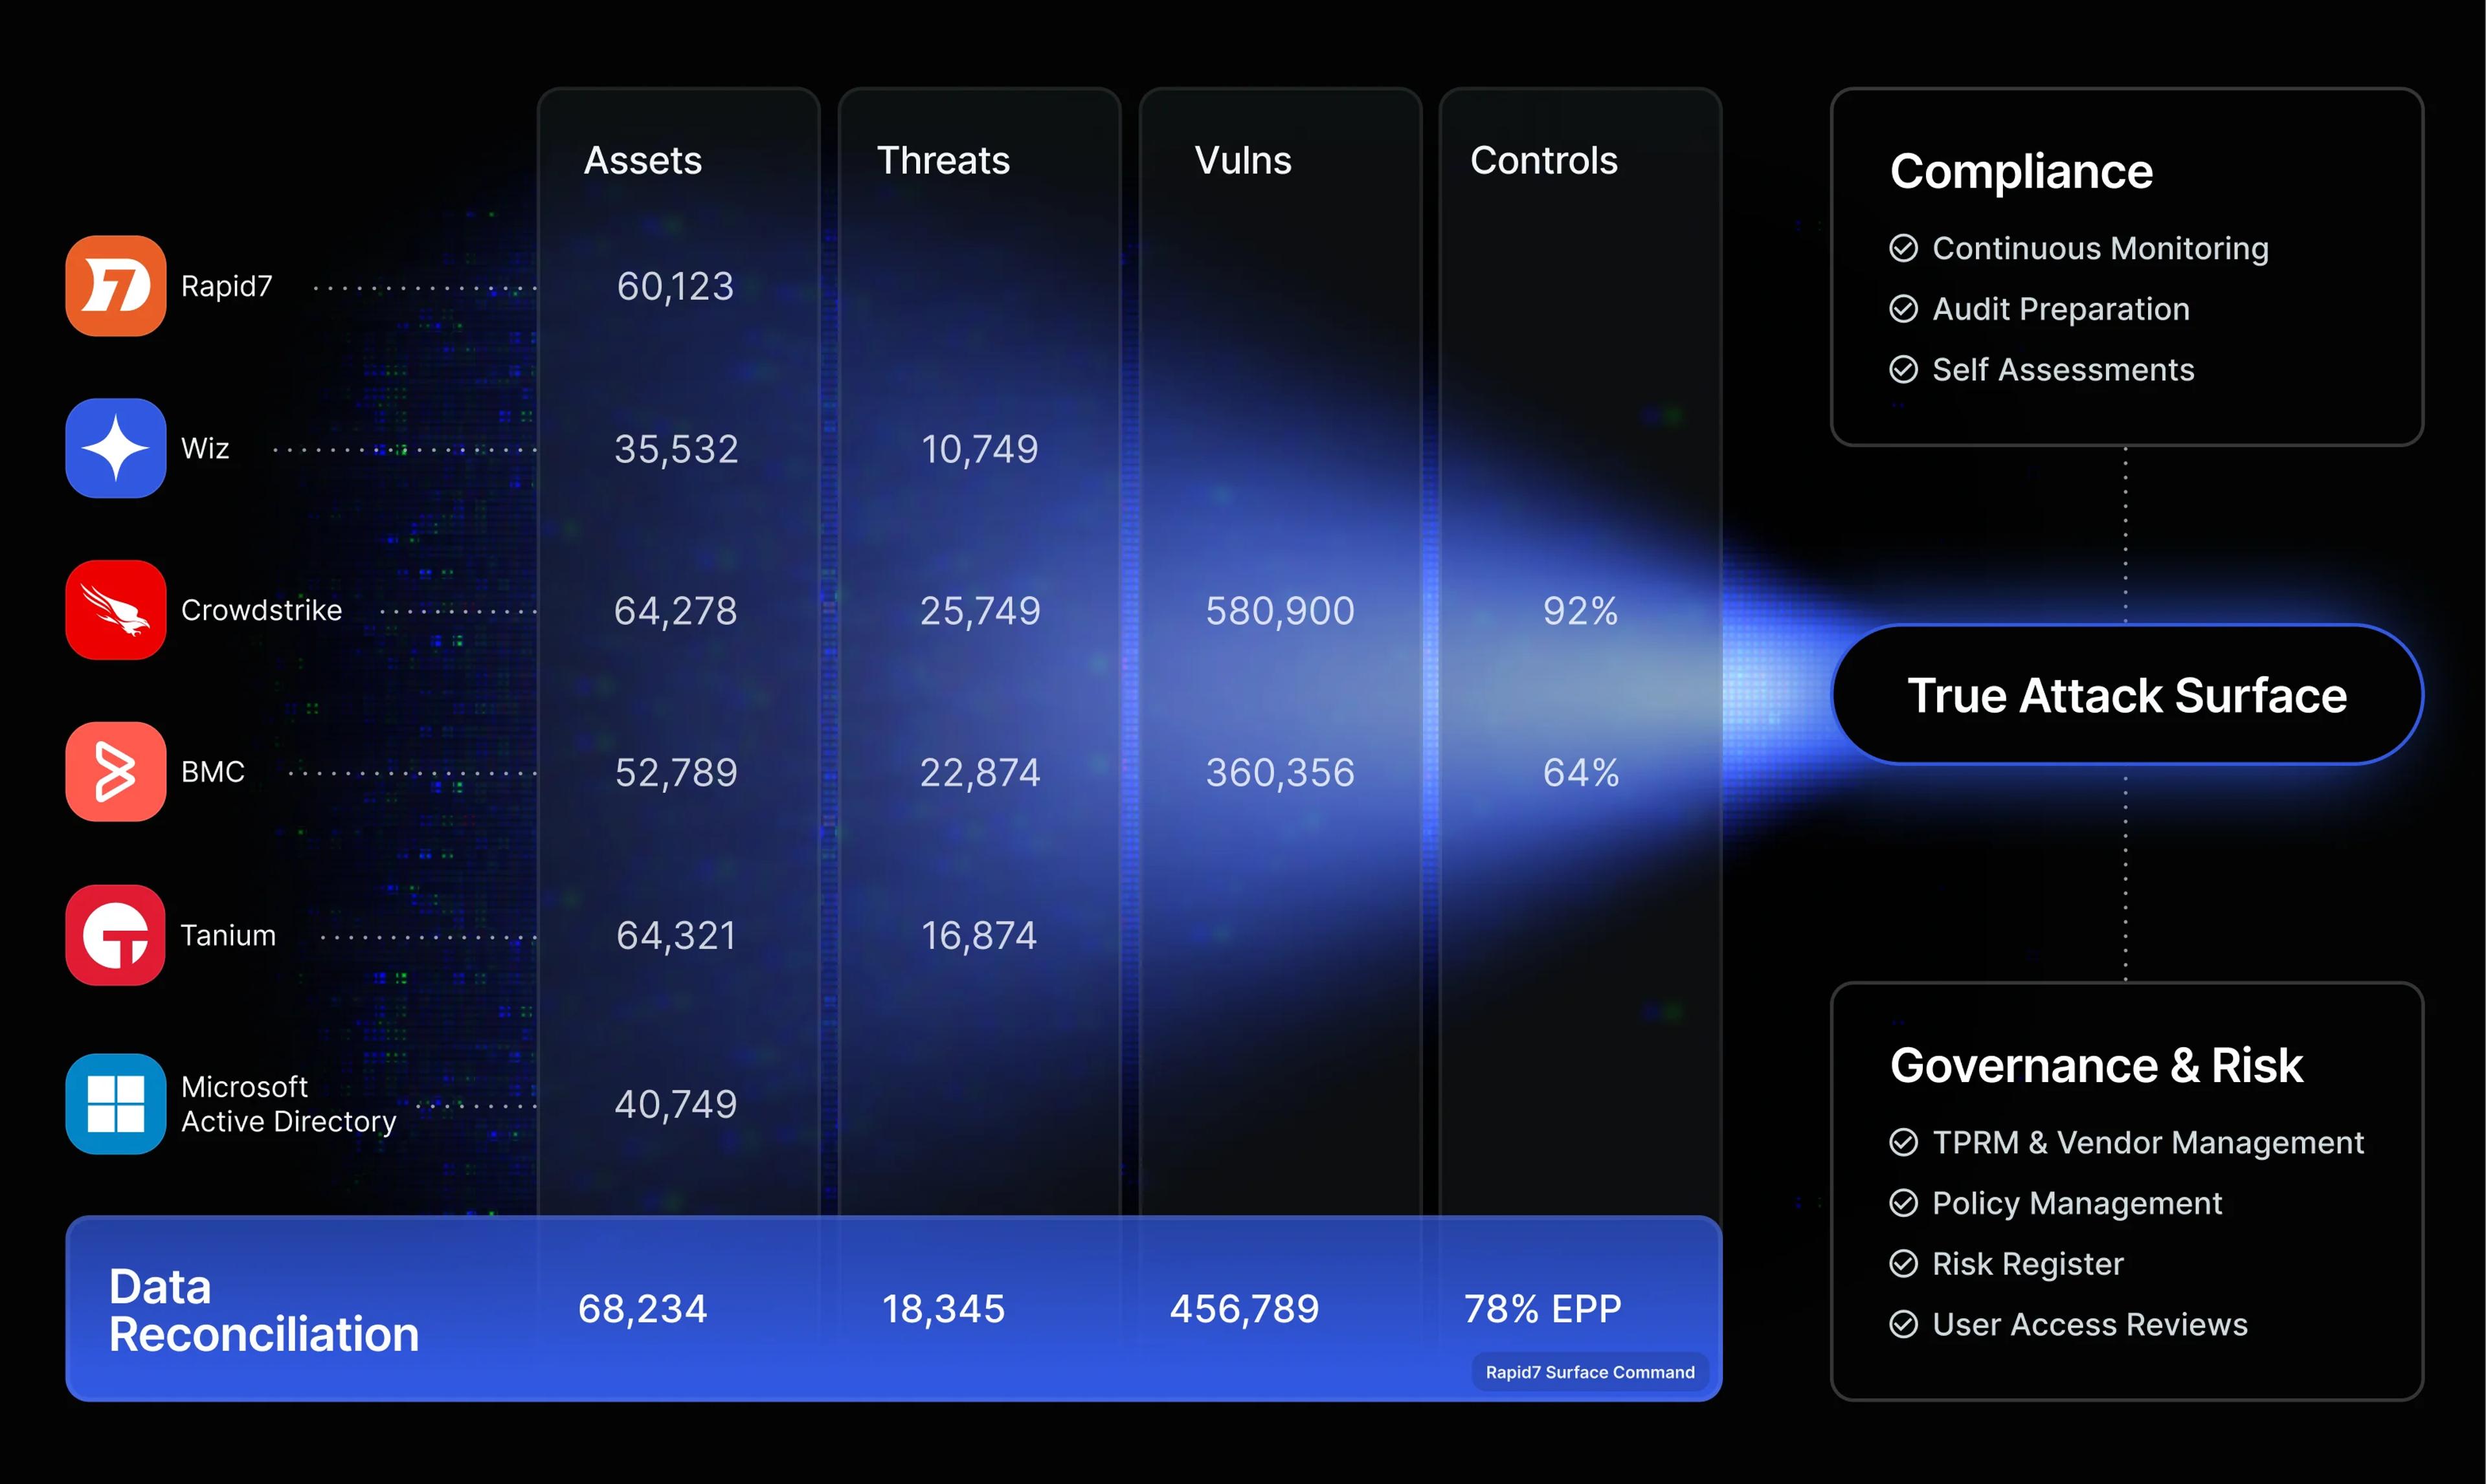
Map evidence once and prove compliance across frameworks
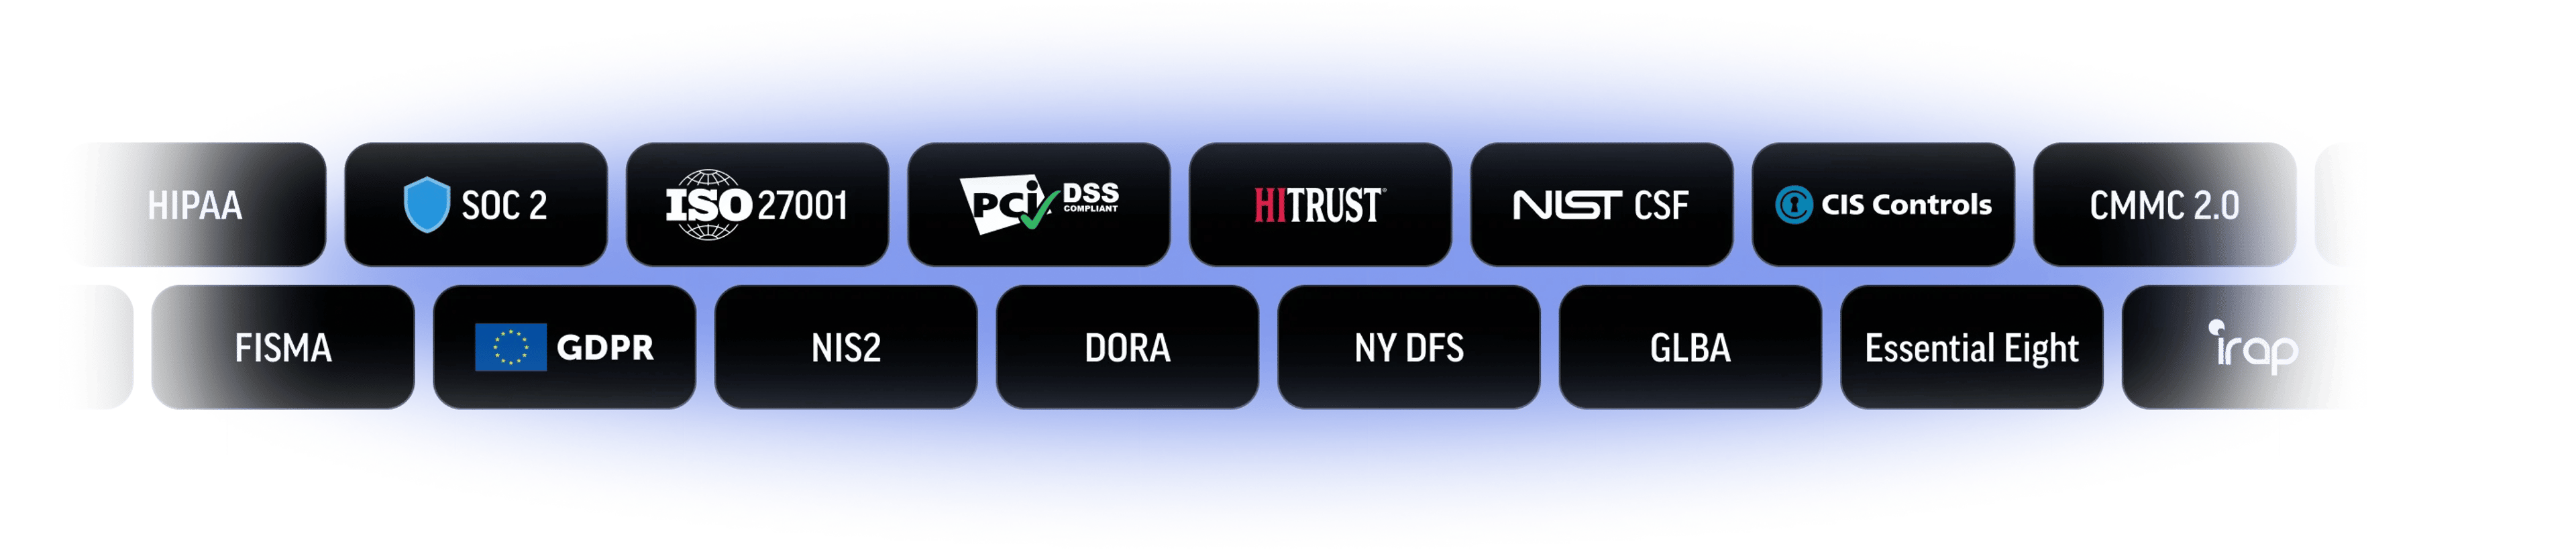
Connect evidence, controls, issues, owners, and third-party risk across multiple frameworks without rebuilding proof manually for every audit.
Built for the CISO’s risk reality
Rapid7 helps leaders govern, prioritize, automate, and prove cyber risk decisions with context from the environment they defend.

Less GRC drag on security
Reduce the manual evidence work that pulls technical teams away from remediation, detection, and response.

Controls tied to real exposure
Understand control health with context from assets, vulnerabilities, threats, vendors, and remediation.

Risk reporting leaders can use
Give executives and the board a clearer view of what changed, what matters, and where risk is being reduced.

Third-party risk in context
Manage vendor risk beside internal controls, exposure data, evidence, and executive risk reporting.
Less GRC drag on security
Reduce the manual evidence work that pulls technical teams away from remediation, detection, and response.
Controls tied to real exposure
Understand control health with context from assets, vulnerabilities, threats, vendors, and remediation.
Risk reporting leaders can use
Give executives and the board a clearer view of what changed, what matters, and where risk is being reduced.
Third-party risk in context
Manage vendor risk beside internal controls, exposure data, evidence, and executive risk reporting.
What CISOs ask when governance, risk, compliance, and third-party assurance are disconnected from security reality
See cyber GRC through a security lens
Request a demo to see how Rapid7 connects governance, risk, compliance, third-party assurance, and remediation to live security context.